

// SECURE AI CONTROL PLANE//
I am Here as
Every agent is calling tools. Who signed off?
Gopher finds every MCP server, puts an identity on every tool call and keeps a replayable record of every action.


Hi, I am Gopher

One agent, four checks, one action stopped.
1M+
Tool calls/s inspected
//Trusted by security, platform and network teams at //

50k+
MCP servers governed
Agents moved faster than the controls.
Written for CISO & security leadership.
Shadow MCP
servers
New servers appear weekly. None are in the inventory.
Calls bypass
every control
DLP, CASB and EDR see a request, not the agent's decision.
No
trail
An agent moved data. Nobody can say who authorised it.
1
// Our claim //
Register of agents and servers Policy on every call. Record of every action.
// What you get //
Controls that grow with the agents.
01
One inventory
Agents, servers and tools with owners and policy state.
02
Policy per call
Identity, scope and payload checked before the tool runs.
03
Replayable actions
An incident is a query, not an investigation.
// HOW WE PROTECT AI //
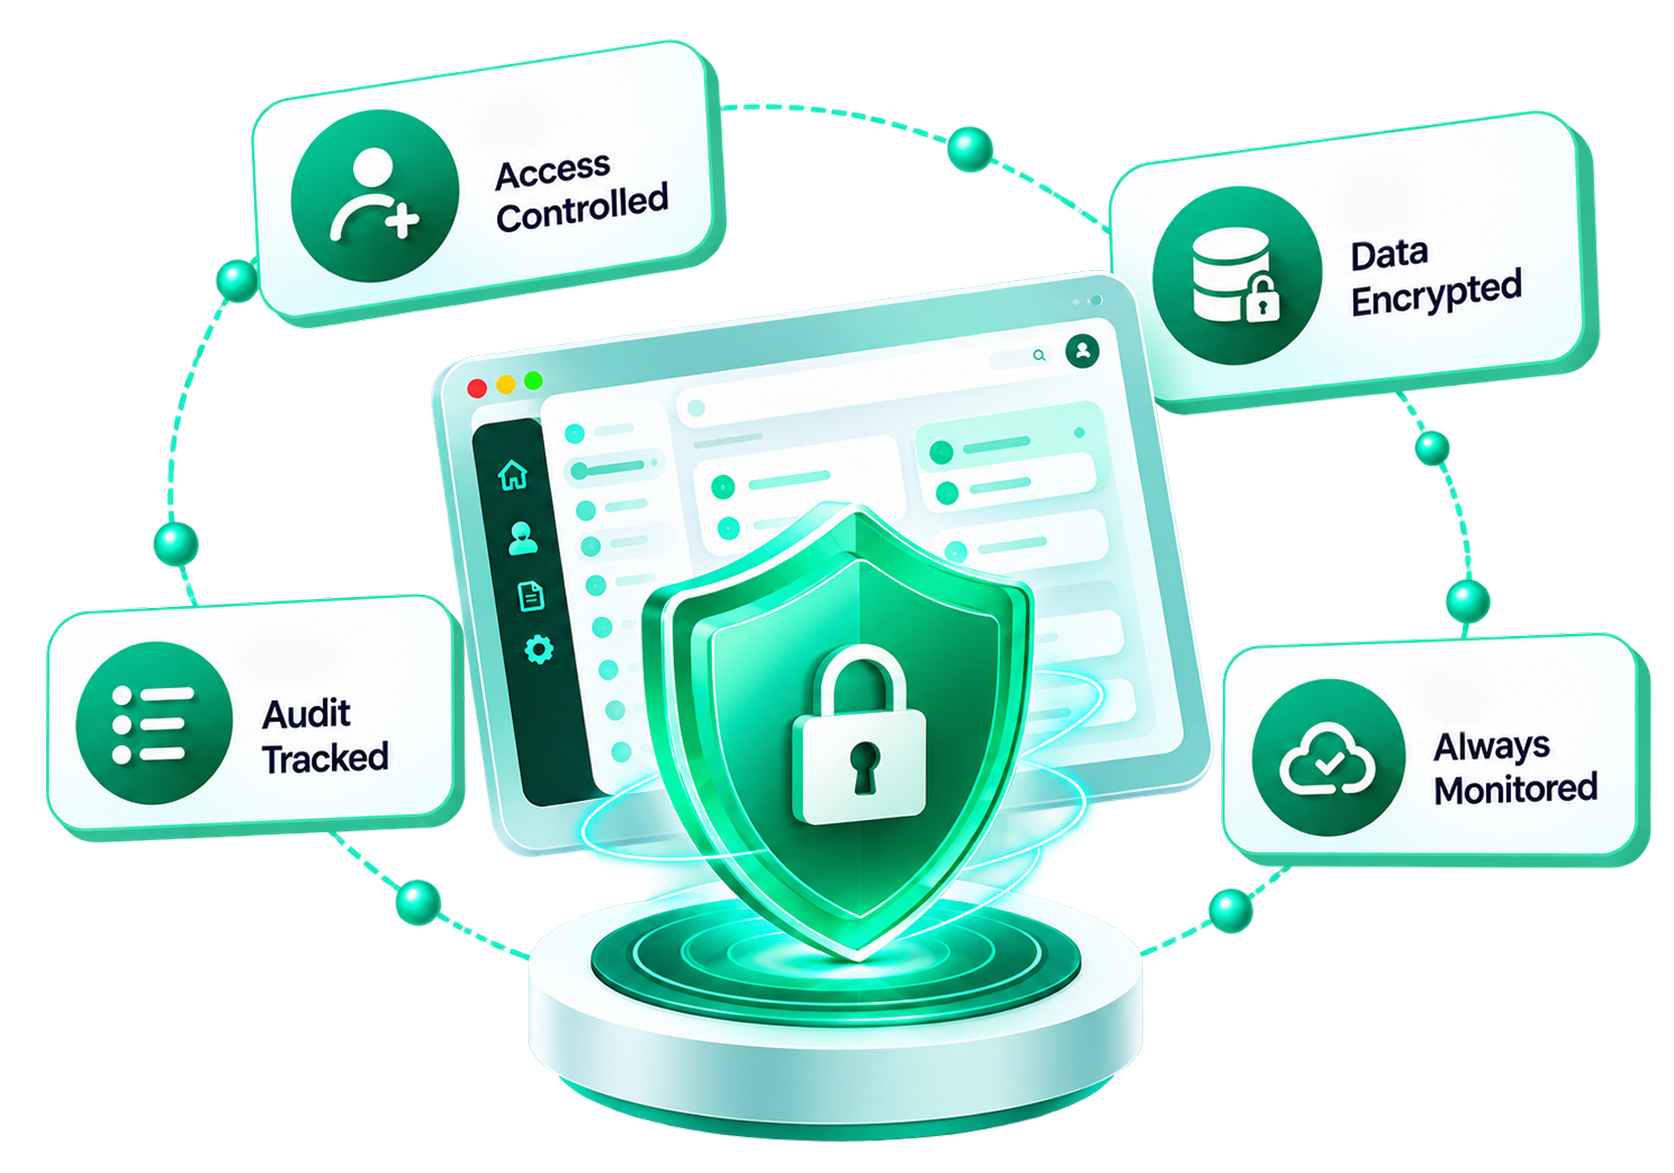
One control plane for every agent, tool call and MCP server.
Gopher sits where an agent's decision becomes an action, and treats that action like a human's.
Book a Demo
// See it live · no signup //
Four clicks through the console.
Find an unregistered server, assign an owner, attach a policy, pull the record.

// THE GOPHER PLATFORM //
Where security leaders usually start.
01
MCP security
Find, gate and audit every MCP server,
registered or not.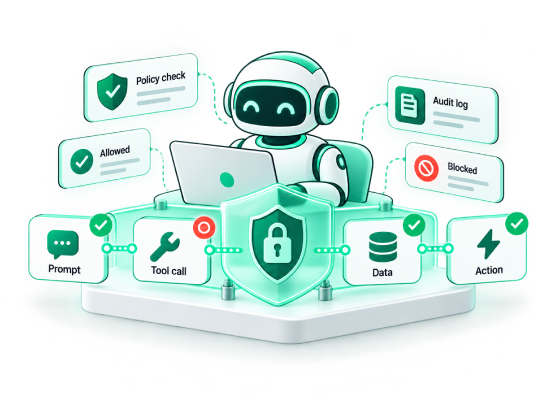
02
Agent security
Policy on the whole prompt → call →
data → action chain.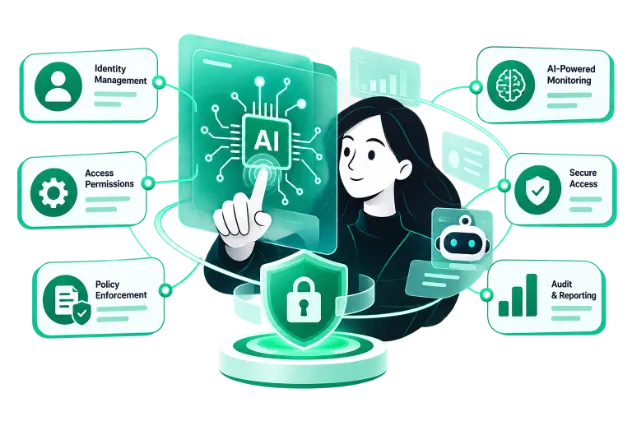
03
AI access control
Identity and least privilege on every
tool call.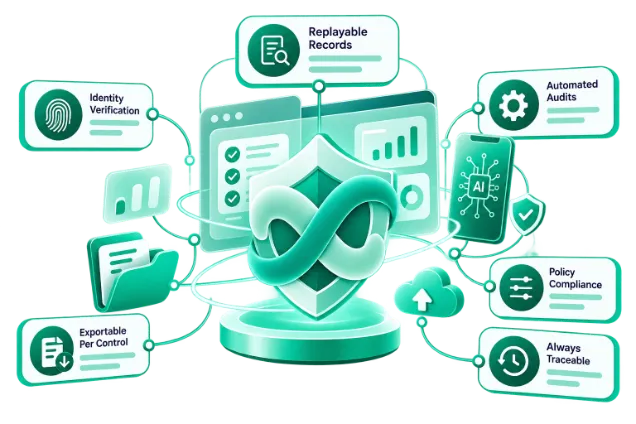
04
AI audit
Replayable records,
exportable per control.
// Certified apps //
Connect your agentic workflows to any enterprise app.
1,000+ certified toolkits. Each is an enterprise app whose tools your agents reach through the control plane, governed and observed.


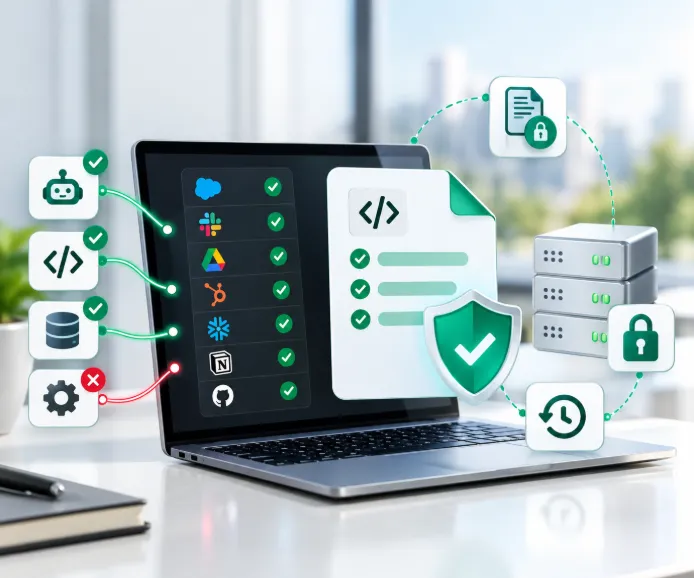
Every tool schema reviewed and pinned
Tool definitions verified and version-locked. Upstream changes can't alter what agents can do.
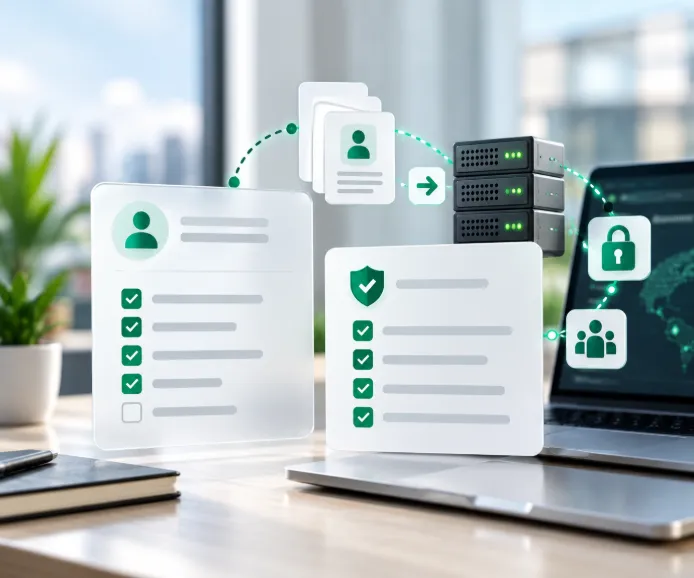
Identity, scope and policy on day one
Per-tool scopes and a starter policy for PII, secrets, money out and destructive actions.
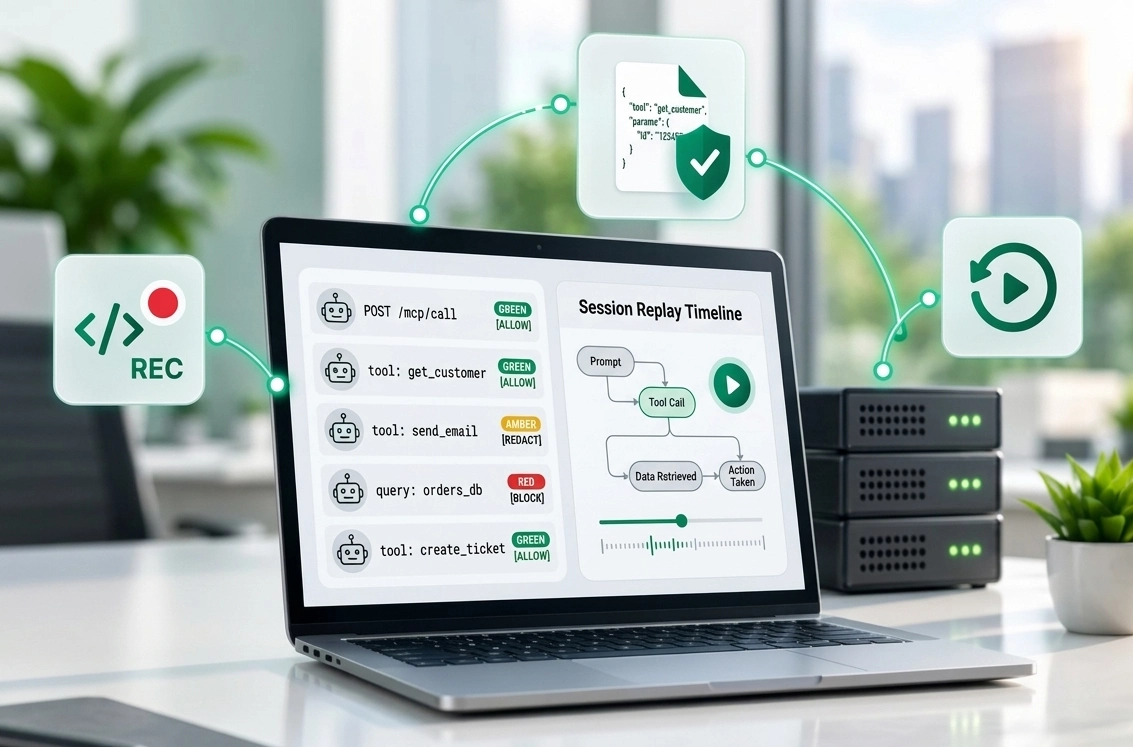
Every call recorded and replayable
Every call lands in the same session record. One trail across all 1,000+ apps.











1,000+
certified toolkits
40k+
tools under policy
0
custom connectors to write


// Proof at scale //
The constraint you answer to shapes the deployment.
 See the deployment →
Financial services
Evidence for examiners on every agent action, and least privilege for agents that touch customer data.
 See the deployment →
Government & defense
Agent governance for classified-adjacent systems. Air-gap ready; no data leaves the boundary.
 See the deployment →
Healthcare
PHI stays inside the scope an agent is allowed to touch, with the record to prove it.
 See the deployment →
Technology
Ship agents fast without a security review queue: policy as code, owned by the platform team.
50k+
MCP servers governed
1M+
Requests per second
10k+
Identities on the mesh
20+
Countries


Eleven MCP servers we didn't know about on the first scan. Two weeks later every call was logged and reversible.

// Testimonials //
What security and platform teams say after the first month.
From top-5 banks to national defense agencies, security and platform teams govern every agent through one control plane.
We point Gopher at an internal API and have a governed MCP server the same afternoon. Security review is a pull request now, not a ticket.
The auditor asked who approved each agent's access. We answered with one export, mapped to the control and signed by the owner.
Our first AI audit took an afternoon. We exported agent access evidence by control.
Security stopped being a queue. Every agent ships with a policy attached.
The bulk-export landed in our SIEM with the whole chain attached. We revoked one scope and the agent kept working.
Eleven MCP servers we didn't know about on the first scan. Two weeks later every call was logged and reversible.
Also from Gopher · Quantum-Safe Networking
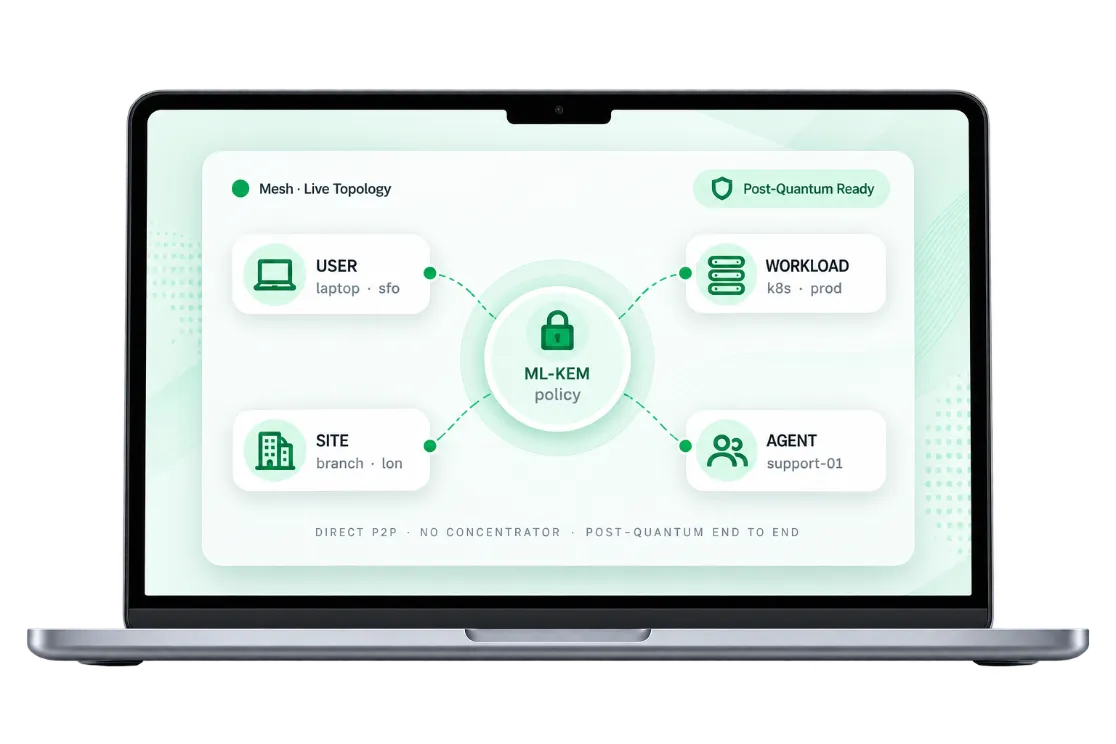
The same policy engine, on the network your agents and people run on.
A post-quantum P2P mesh for every user, workload and site. Same identity, policy and audit as the control plane.
// FAQ //
Frequently asked questions
Answers about the Secure AI Control Plane and Quantum-Safe Networking. If yours isn't here, ask us — a security engineer replies.
What is the Secure AI Control Plane?
One platform that connects agents to any enterprise app through MCP, with identity, policy and audit on every tool call.
How is it different from a prompt filter or gateway?
It inspects four things per call: prompt, tool call, data access and action. It allows, redacts or blocks each one.
Does it work with my existing MCP servers?
Yes. Any MCP server, client or model. Registered servers get policy; unregistered ones are discovered and flagged.
What attacks does it stop?
Tool poisoning, prompt injection through tool results, over-scoped access, data exfiltration and destructive actions.
What happens when a threat is detected?
The action is blocked, your team is alerted and the full session is recorded for replay.
What compliance standards does it support?
SOC 2, ISO 27001, GDPR and HIPAA, with evidence exportable per control and period.
How quickly can I deploy?
Minutes. Point it at a schema or an existing server. No changes to agents or models.
How is it priced?
By deployment size and requirements. Book a demo for a quote.
What is Quantum-Safe Networking?
A zero-trust P2P mesh with post-quantum encryption between every user, workload and site.
Is it a VPN?
No. Paths are direct, peer to peer, with no concentrator. Access is per identity and per task, not per network.
What makes it quantum-resistant?
ML-KEM key exchange on every path, so traffic captured today can't be decrypted later.
Does it replace my PAM and segmentation tools?
It can. Just-in-time privilege, micro-segments and SASE edge run on one policy engine.
Do I need new hardware?
No. Peers join with a lightweight agent. Segments and routes are configuration in your pipeline.
How does it fit with the Secure AI Control Plane?
Same identity, policy and audit. An agent's network path is as scoped as its tool policy.
What compliance standards does it support?
SOC 2, ISO 27001, GDPR, HIPAA and CNSA 2.0 timelines, with one record per session exportable by control.
How is it priced?
By peers and sites. Book a demo for a quote.

// Stay Informed. Stay Ahead. //
Bring your riskiest agent. We'll show you what it's calling.
Thirty minutes on your own traffic. You leave with an inventory of every server and tool call we can see.